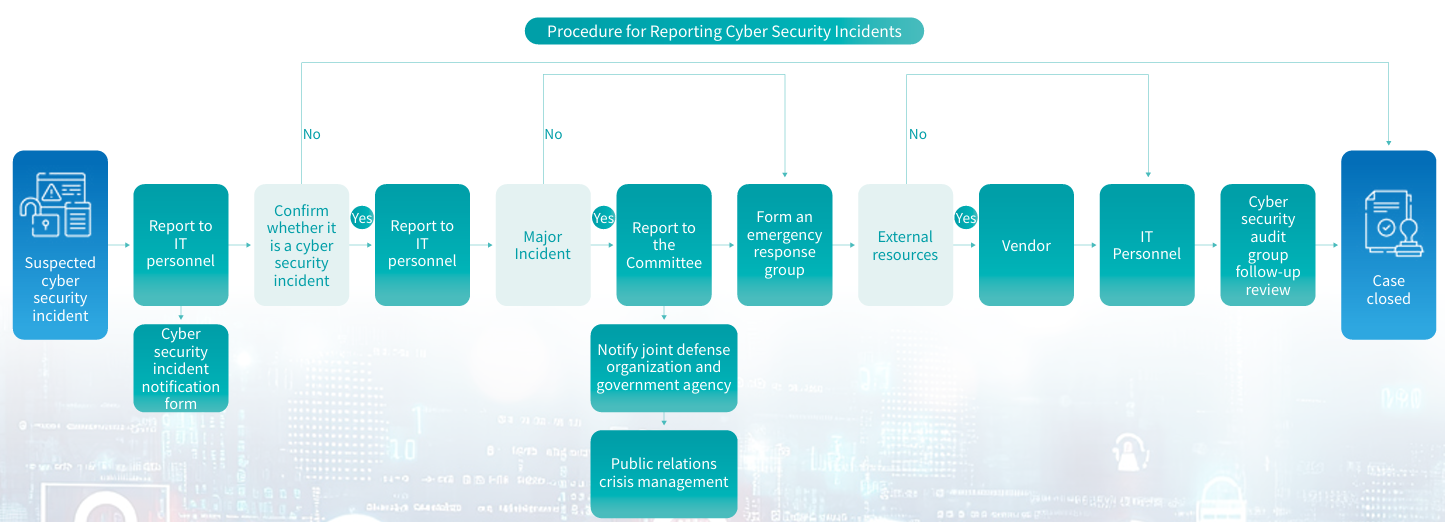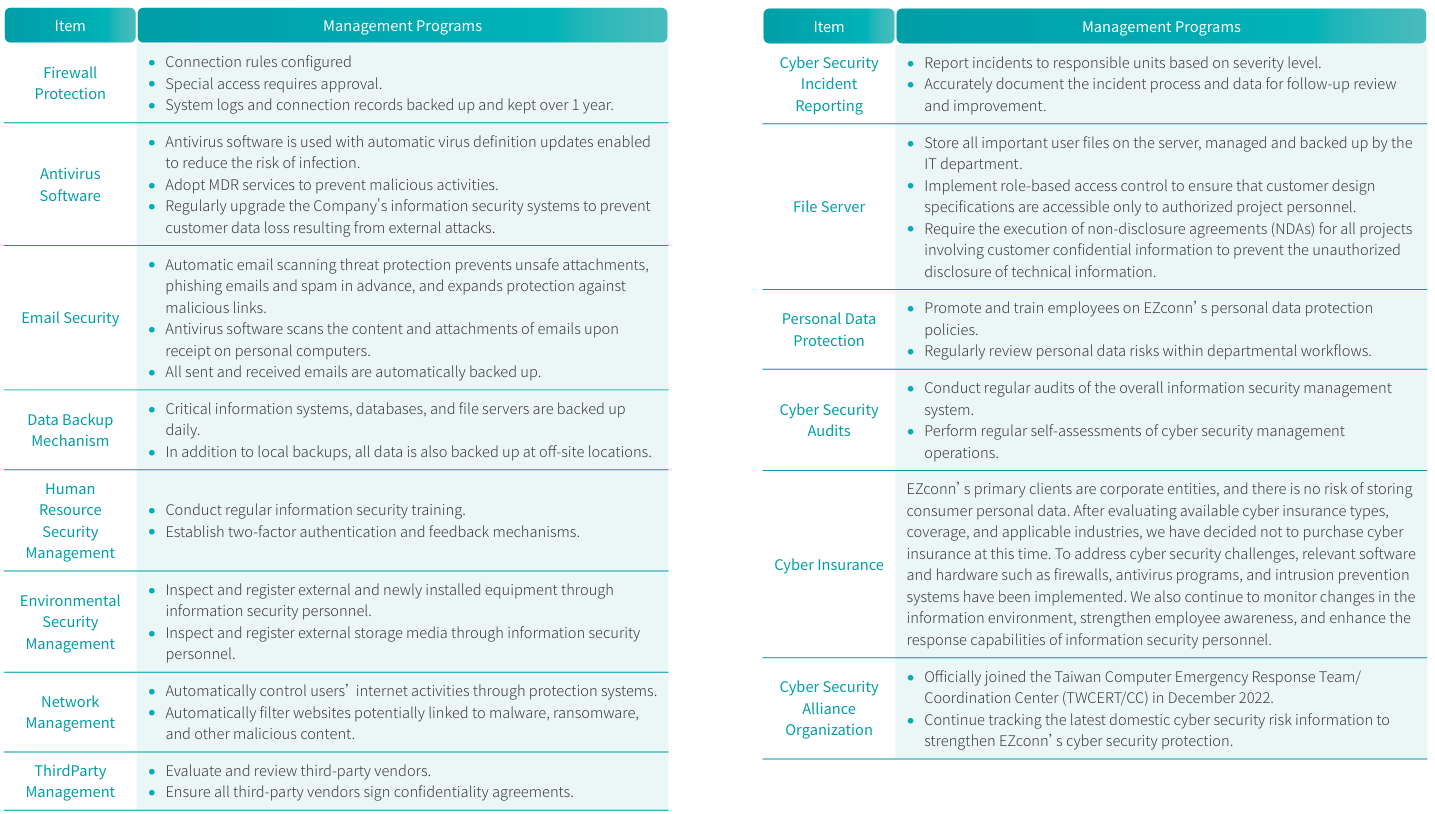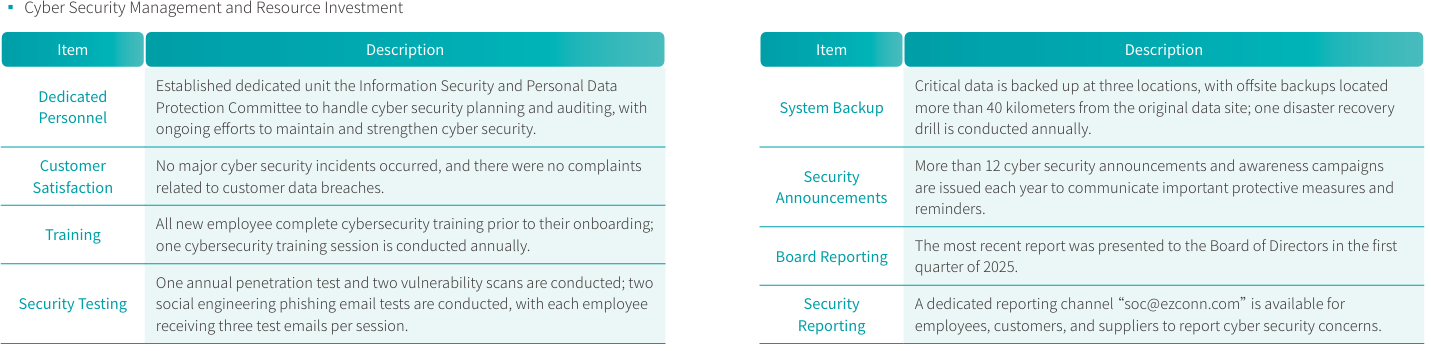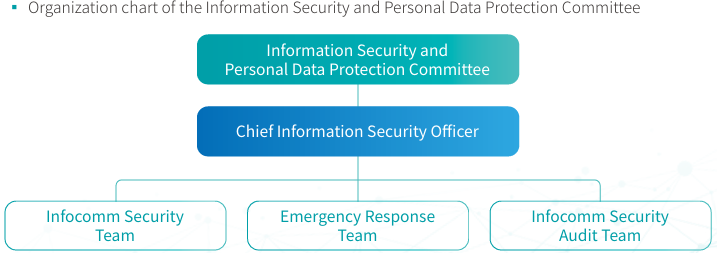
The Infocomm Security and Personal Information Protection Committee is established in order to strengthen the Company's Infocomm security management and ensure the security of data, systems, communication and network. The CEO is the convener of the committee, and the Infocomm Security Officer is responsible for implementation and reports to the board meeting once a year. The organization team includes the Infocomm security team, emergency response team, and the Infocomm security audit team. The primary goal is to establish a safe and reliable computerized operating environment to ensure the confidentiality, integrity and availability of the Company's information assets (software, hardware, computer data, information environment and personnel), and prevent them from being damaged by various internal and external threats, so as to enable the Company's information system to operate continuously. In addition, we provide support and commitment to the management in terms of protecting personal data according to the law based on the Personal Data Protection Act and its implementation rules.
The responsible unit of the Infocomm security team is the Information Department, which has one information manager, one full-time Infocomm security administrator and several professional information personnel. It is responsible for the construction of the Infocomm security system, including network management and system management. At the same time, it continuously reviews and evaluates the trend of changes in the information environment, and evaluates information security risks and protections to ensure the continuous and effective operation of the internal information security management mechanism.
The emergency response team is a task-based team, responsible to coordinate with each person in charge for key business during and after disasters, while implementing the rescuing, evidence investigation, cleanup, and recovery. Every year, the team convene the related personnel for disaster drills, seeking to reduce the damage from disaster, and have the disaster site to resume the basic operation in the shortest time when incidents incur.
The Infocomm security audit team is responsible for supervising the implementation of internal Infocomm security. If there is any deficiency found in the audit, the team will require the inspected unit to propose relevant improvement plans and specific measures, and regularly and continuously track the improvement results to reduce internal Infocomm security risks.